Essential cookies only — Cookie Policy.
Bulk password generation for IT admins and DevOps teams. CSV, JSON, and plain text. Nothing leaves your browser.
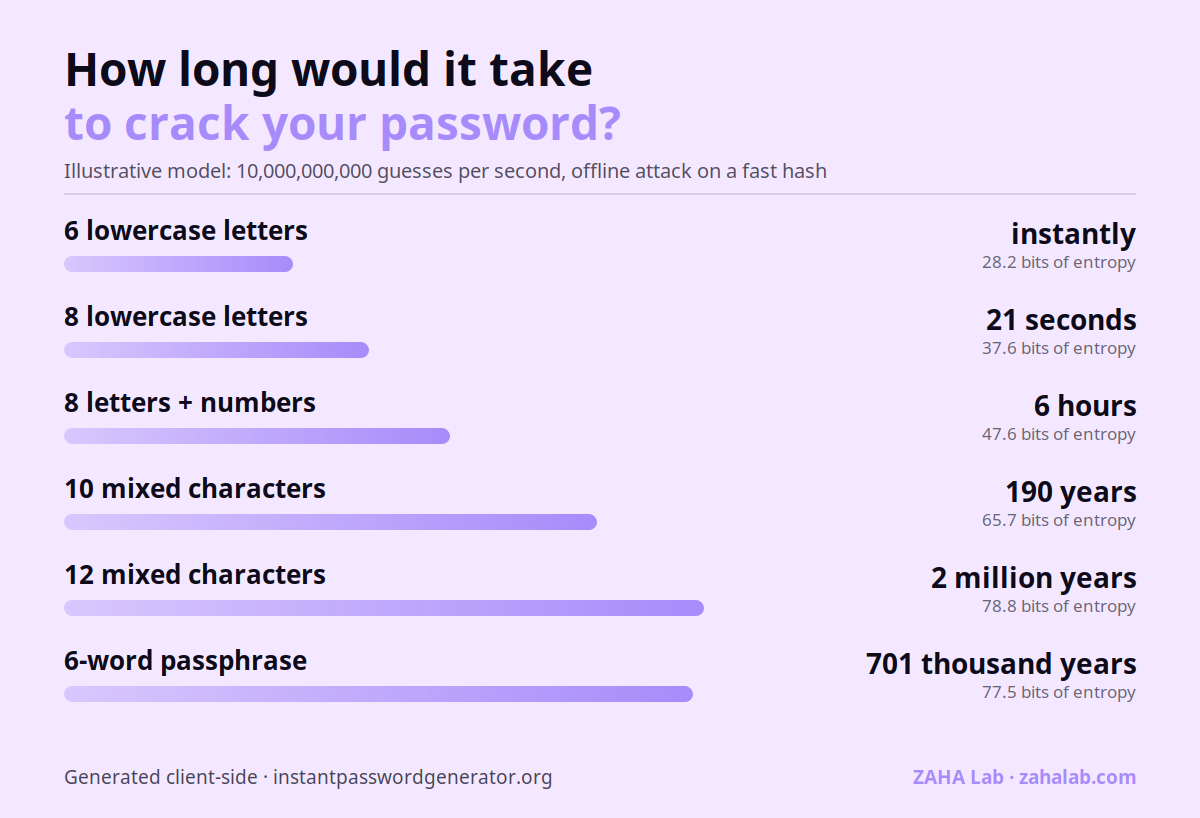
A short password falls instantly, however random it looks. The table and chart below model an offline attack at 10,000,000,000 guesses per second against a fast hash — the same maths a cracking rig actually runs.
| Password pattern | Time to crack | Entropy (bits) | Verdict |
|---|---|---|---|
| 6 lowercase letters | instantly | 28.2 | Weak |
| 8 lowercase letters | 21 seconds | 37.6 | Weak |
| 8 letters + numbers | 6 hours | 47.6 | Moderate |
| 10 mixed characters | 190 years | 65.7 | Moderate |
| 12 mixed characters | 2 million years | 78.8 | Strong |
| 6-word passphrase | 701 thousand years | 77.5 | Strong |
Assumes uniform random characters and no rate limiting. Password reuse or a breach database shortcut all of the above — which is why a unique password per account matters more than length alone.
Press Generate — up to 50 CSPRNG passwords instantly.
Common workflows where bulk generation saves significant time.
Generate 50 unique passwords, export CSV, import with PowerShell New-ADUser. Set ChangePasswordAtLogon for all accounts.
Generate replacement credentials for service accounts on rotation schedule. JSON output integrates directly with secrets management pipelines.
Populate test databases with realistic unique credentials. Numbered format maps directly to user IDs for automated fixture generation.
After a credential compromise, bulk-generate replacements for all affected accounts immediately. CSV export for rapid controlled distribution.
Key parameters across the major standards — all auto-configured in the Iron Vault Keys Policy Builder.
| Framework | Min Length | Rotation | Composition Rules | Breach Check |
|---|---|---|---|---|
| NIST SP 800-63B 2025 | 15 chars | SHALL NOT (prohibited) | SHOULD NOT (discouraged) | SHALL (mandatory) |
| PCI-DSS v4.0 | 12 chars | 90 days (no MFA) / None (MFA) | Alpha + numeric required | Not specified |
| ISO/IEC 27001:2022 | Org-defined | Org-defined | Org-defined | Recommended |
| HIPAA (45 CFR 164) | Not specified | Periodic recommended | Not specified | Not specified |
| Cyber Essentials (NCSC) | 8 chars | On compromise only | None required | Not specified |
Sources: NIST SP 800-63B July 2025 · PCI SSC v4.0 March 2022 · ISO/IEC 27001:2022 · HHS HIPAA guidance · NCSC Cyber Essentials 2024. The bulk generator defaults to 20 characters — exceeding all framework minimums simultaneously.
Store and distribute generated passwords securely with NordPass Business. Role-based access, audit logs, and encrypted sharing for your entire team.
Start Free Trial →Strong passwords combined with zero-trust network access. NordPass integrates with SSO to enforce least-privilege across distributed IT teams.
Explore NordPass →NordPass Enterprise includes automated password rotation, breach monitoring, and Active Directory sync. Centralised oversight for compliance reporting.
NordPass Enterprise →crypto.getRandomValues() — the speed badge shows the actual generation time, typically under 2ms for 50 passwords.Import-Csv users.csv | ForEach-Object { Set-ADAccountPassword -Identity $_.index -NewPassword (ConvertTo-SecureString $_.password -AsPlainText -Force) }. Always set -ChangePasswordAtLogon $true.crypto.getRandomValues() — the browser CSPRNG, seeded from OS hardware entropy. No password is transmitted to any server. Verify in DevTools → Network while generating — zero requests are made.crypto.getRandomValues() call, leaving all others unchanged.0 / O, 1 / l / I. Useful when passwords are distributed in print or verbally. Slightly reduces entropy — only enable when readability is required.The guides and tool on this site are written by Alex Chen, our security editorial team in enterprise credential management, Active Directory automation, and NIST SP 800-63B implementation across UK and US enterprise environments.
All technical claims are sourced from primary documents — NIST publications, NCSC advisories, Verizon DBIR, and IBM Cost of Data Breach Report. Content is reviewed whenever security standards evolve.
Read more about us →crypto.getRandomValues() — no server contact